

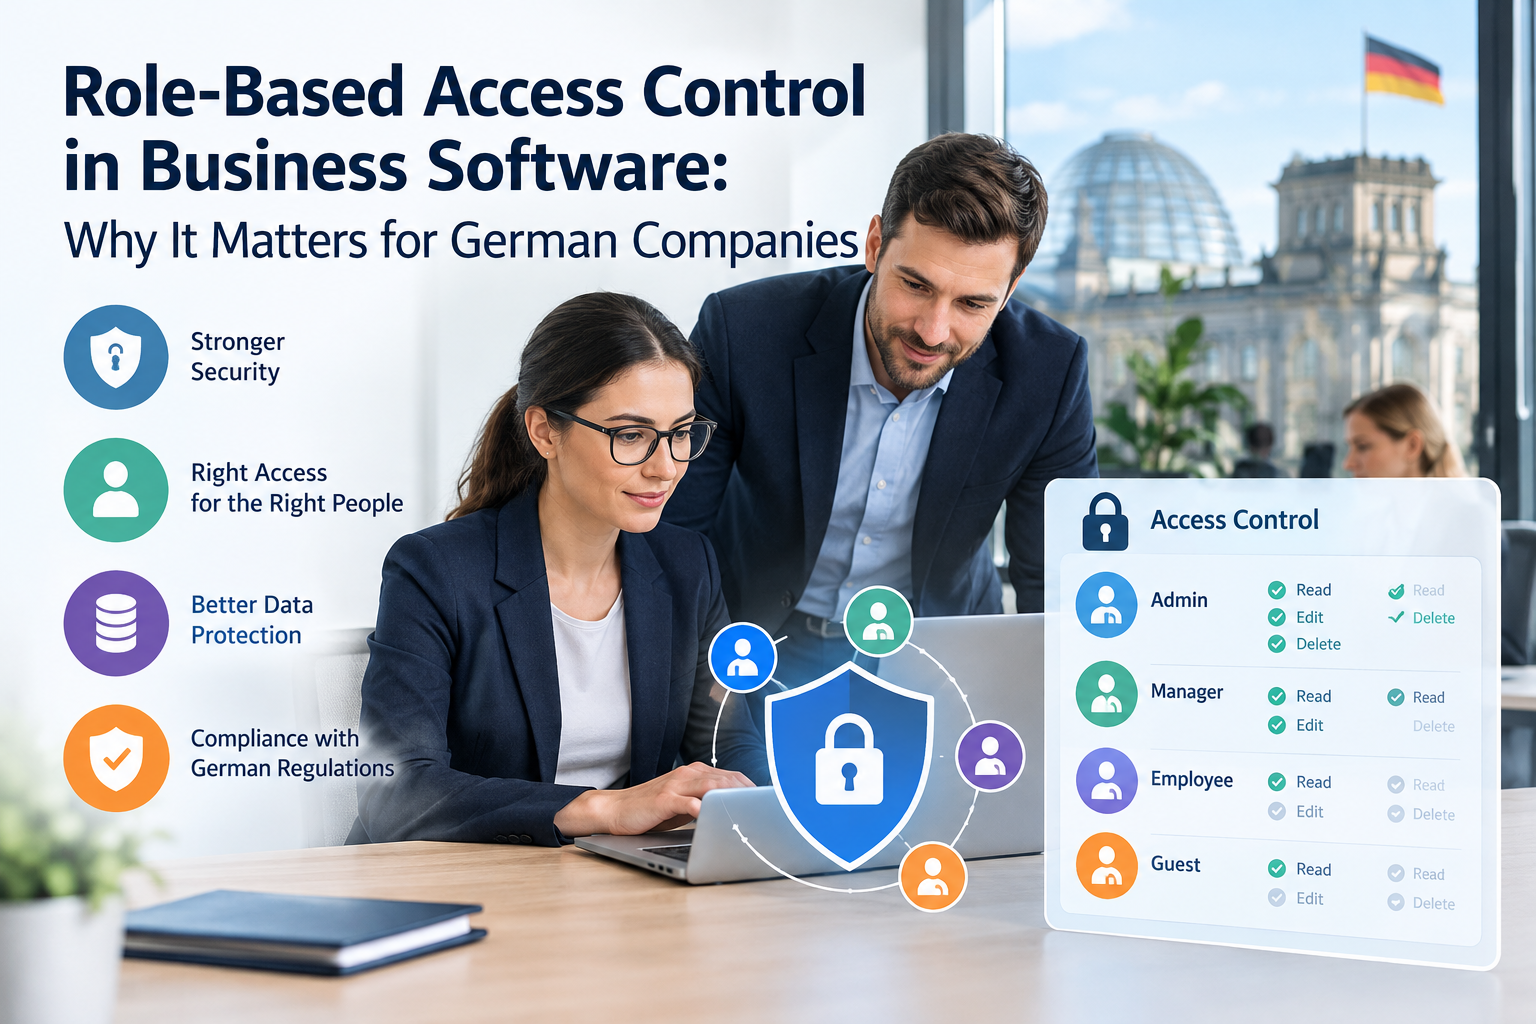
Role-Based Access Control in Business Software: Why It Matters for German Companies

A new colleague joins the sales team on Monday and, by Tuesday, can open payroll files, change supplier bank details and export the full customer list. Nobody planned that. The account was simply copied from a long-serving employee, whose access had grown over ten years and was never trimmed. Situations like this are common in companies that have never decided, in a structured way, who should be allowed to do what inside their software.
Role-based access control, usually shortened to RBAC, is the standard answer. It ties permissions to roles that reflect real jobs, instead of to individuals one by one. This article explains how it works, why it carries extra weight for German companies, and how to introduce it without creating a bureaucratic mess.
How role-based access control works
The idea is straightforward. Instead of deciding for each person which screens they may open and which records they may change, you define roles such as "sales representative", "accounts payable clerk", "warehouse supervisor" or "system administrator". Each role carries a defined set of permissions. People are then assigned one or more roles, and they receive the permissions that come with them.
The benefit shows when circumstances change. When someone moves from sales to customer service, you swap their role and the right access follows. When someone leaves, removing their roles removes their access. Compared with managing hundreds of individual permissions, this is quicker, more consistent and far easier to review.
Permissions in a well-designed system are more than a simple yes or no to a whole application. They can distinguish between viewing, creating, editing, approving and deleting. They can also be limited by scope: a regional sales manager sees customers in their own region, a project lead sees their own projects, a branch employee sees only their branch. Some systems add conditions, such as allowing a payment approval only up to a certain value. This finer control is where the practical value lies.
Why it matters particularly in Germany
Several features of the German and European business environment make structured access control more than a technical nicety.
The GDPR requires organisations to protect personal data with appropriate technical and organisational measures, and it expects that data is processed only for specified purposes and by people who need it. Customer records, employee files and contact details held in business software are personal data. If every employee can see all of it, demonstrating that you limited access to what was necessary becomes difficult. RBAC gives you a clear, documentable answer to the question of who can see what, and why.
Employee data deserves particular attention. HR records, salary information, absence data and performance notes are sensitive in practice and heavily protected in principle. Works councils often take a close interest in how employee data is handled and who can access it, and in many companies they have co-determination rights over systems that could monitor staff. A transparent role model makes those discussions easier, since it shows exactly who can see which categories of information.
Financial controls point the same way. Companies are expected to maintain internal controls that reduce the risk of errors and fraud, and a basic principle is separation of duties: the person who creates a payment should not be the one who approves it, and the person who sets up a new supplier should not also release payments to them. RBAC is the mechanism by which software enforces that separation. Which specific control requirements apply depends on the company's legal form, size and sector, and your auditor or finance lead can tell you what matters in your case.
Finally, there is the commercial dimension. B2B customers increasingly ask suppliers about access controls in security questionnaires. Being able to describe a clear role model is a practical advantage.
Designing roles that work
The common failure is to start from the software's menu rather than from the business. A better approach begins with how people actually work.
List the main job functions in the company and, for each, the information and actions they need to do their jobs. Resist the temptation to be generous. Apply the principle of least privilege: give each role the minimum access required, and add more only when someone demonstrates a genuine need. It is easier to widen access later than to discover after an incident that half the company could read sensitive records.
Keep the number of roles manageable. Too few, and roles become broad and over-permissive. Too many, and the model turns into individual permissions under another name, which defeats the purpose. A useful pattern is to build roles from smaller building blocks, such as a base role for all employees, a departmental role and a limited number of special rights for tasks like approvals or exports.
Pay attention to the awkward cases. Temporary cover during holidays, staff who work across departments, external consultants and shared mailboxes all need a considered answer, such as time-limited role assignments, rather than informal password sharing.
Common mistakes
Several problems appear repeatedly. Access accumulates as people change jobs and nobody removes their old rights, a drift sometimes called privilege creep. Administrator accounts are handed out too freely, or shared between several people so that actions cannot be traced to anyone. Access control is enforced only in the interface, by hiding a button, while the underlying function can still be called directly. And roles are designed once and never reviewed, so the model slowly drifts away from how the business actually operates.
Building RBAC into custom and existing software
With packaged software, the available role options are set by the vendor. Check how flexible they are: can you define your own roles, restrict by region or record type, and export a report of who has which rights? Where the standard model is too coarse, you may need to supplement it, for example through the central identity system.
With custom applications, role design should be part of the requirements from the start, and enforcement must happen on the server side for every request, not just in the screens users see. Companies commissioning bespoke software often work with providers of software entwicklung to turn a role model into working access rules, including integration with the company's single sign-on and identity management. Make sure the specification covers how roles are assigned, who may assign them and how changes are logged.
Auditability is part of the design too. The system should record who changed permissions, when and why, and who accessed sensitive records. That record is valuable both for investigating incidents and for showing regulators or customers how access is controlled.
Keeping the model healthy
An access model is not finished once it is configured. Schedule regular access reviews, for example every six or twelve months, in which department heads confirm that each person's roles are still appropriate. Tie role changes to HR events, so that joiners, movers and leavers trigger updates automatically instead of relying on someone remembering. Pay special attention to administrator and approval rights, which deserve more frequent review.
When the requirements are being agreed, in-person workshops with the departments involved often produce better results than a document passed around by email. Some companies therefore prefer partners nearby, such as those offering software entwicklung berlin or software entwicklung hamburg. Location is a convenience, and experience with access models in comparable companies matters more.
Conclusion
Role-based access control matters because it turns a vague intention, that people should see only what they need, into something a company can define, enforce and demonstrate. For German businesses handling personal data, employee information and financial approvals, that clarity supports data protection, internal control and customer trust at the same time.
A practical first step is to choose one important application and list its current users alongside what each can do. Compare that list with what their jobs require. The gaps you find will show where roles are too broad, and they provide a concrete starting point for designing a cleaner role model.
